It might be possible to fool it.
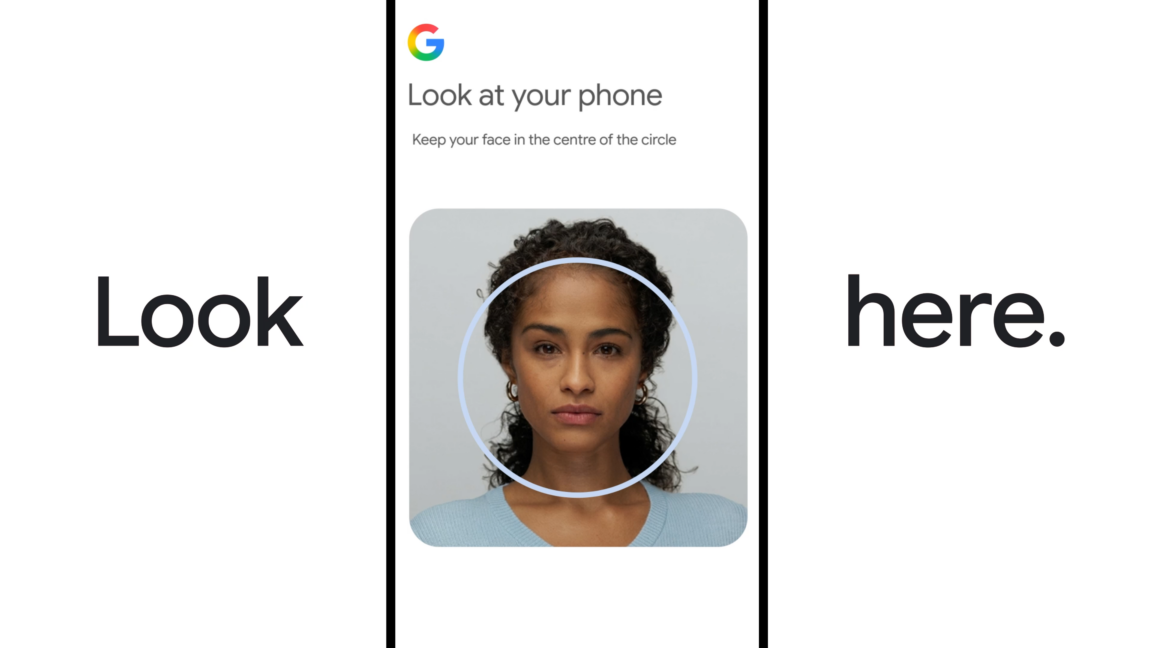
More important, it’s normalizing use of facial recognition in everyday situations. This is a very invasive tech and prime for abuse by increasingly totalitarian governments.
Yeah, thanks but no thanks.
The biggest thing I’ll use is fingerprint on my phone, caus its comfy, and quickly disabled should the need arise
It is good practice to create a different password for each service. That way, if one service is compromised, your adversary cannot use that password to unlock everything else.
That may sound onerous, but thanks to selfie-login technology, you can instead simply use a different face for each account.
Did i just time travel or is this the feature i have been refusing to use on my phone for almost a decade?
Yeah November 2017; 8 years ago
Is this implemented very different technologically speaking?
faceId is completely in device. This is a video that is sent to google to process
Maybe its “unlocking” stuff on your desktop browser with your phone, like the new captchas where you have to scan a QR and receive a code via SMS (seriously google, what the heck)
As I’ve said before: HOW ABOUT NO
So what do we do about my evil twin brother who is a supervillain?
I didn’t believe this was a problem until I watched my wife and her twin sister unlocking each others phones (they aren’t identical but they do look quite a lot alike)
Time for graphene and protonmail. They should at least take another 15y to enshittify to this point.